 Posted by
Firesheep
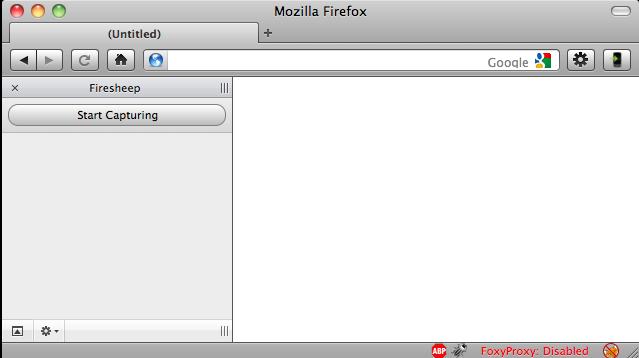
The add-on which goes in the left hand side bar of the Firefox web browser can allow a user to capture login information to Facebook accounts, twitter accounts, and any other website login that is not secured with SSL (https). When you login to your Facebook account, a cookie is sent back to your computer to be used for future logins. Someone using Firesheep for Firefox can simply click a button that says “start capturing” and steal your login details. All they have to do is then click on your Facebook image and they will be logged in as you.
This works the same for any website whose login page does not use full end-to-end encryption. For example, when you login to Gmail, you will see the URL has “https://” in front of it. That means that Gmail is secure, and your login information can not be stolen using Firesheep. However for sites like Facebook, Twitter, Flickr, etc (sites that only show “http” (without the “s” at the end), when logging in, your login details can easily be compromised by someone using Firesheep. Other websites that use the safer https protocol are banking sites, credit card companies, most popular email hosts, and government websites.
The Firesheep addon is made available at http://codebutler.github.com/firesheep/
Firesheep is not the only way hackers can steal your login information through this method. There are other more sophisticated hacking programs that allow hackers to do the same thing.
The reason Toorcon 12 decided to release this potentially dangerous software is to make companies like Facebook aware of the issues that come about when they do not use SSL. Hopefully these companies realize the potential dangers that their users are being exposed to, and fix this problem.